The Journey from Traditional Networking to Cloud Networking (Azure)

I’ve spent a lot of years doing “traditional” networking. ASIC-based switches, hand-built BGP adjacencies, both sides of every connection configured and verified before I’d trust it. So when I recently went deep into deploying Cisco FTDv firewalls as Network Virtual Appliances (NVAs) into an Azure Virtual WAN vHub, I expected the usual: configure my side, configure Azure’s side, watch the neighbour come up.

That’s not what happened. And that gap between what I expected and what actually happens is, I think, the single most important thing to explain to any network person making this jump. So that’s where I’m going to start.

Azure Doesn’t Want You to Touch It, and That Feels Like a Trust Issue

Here’s the thing that will throw you off if you’ve done “real” networking for a while: in Azure Virtual WAN, you don’t configure the other side of the BGP relationship.

Enable Routing Intent on the Azure Portal, and Azure will start BGP peering with your NVA. You will never see a BGP neighbour listed in the portal for it. Not because something’s broken — because Azure never asked you to configure one. The Azure vHub router’s ASN isn’t something you set either; it’s Azure system-assigned the moment the hub gets created. Make sure you’re aware of these Azure ASN reservations so you don’t accidently use them (internet search “azure reserved asn numbers”).

With Routing Intent, there are no Azure route tables to babysit either. Routing Intent is a one and done affair.

If you’re coming from traditional networking, this is going to feel like a trust issue. You’re used to being able to see both sides of an adjacency. In Azure, half of it is invisible to you by design. My advice: don’t fight it. Follow the vendor’s Azure-specific onboarding document (in my case, Cisco’s FTDv guide) to the letter, and stay away from general Azure BGP documentation while you’re doing it. The general docs describe a different mental model and will just confuse you mid-deployment.

The IP Address That Isn’t “For Example”

Buried in the Cisco documentation is a line that says “For example: 168.63.129.16.” I want to flag this specifically because I think it’s a trap.

168.63.129.16 is not an example. Type that exact address. It’s Azure’s “magic” virtual IP — a fixed address, consistent in every single Azure region, that serves as the dedicated endpoint for DNS, DHCP, and health probes. If you read past that line assuming it’s a placeholder like most documentation examples are, your health probe will never work, and neither will your BGP pairing, because Azure won’t consider your NVA operational until that probe succeeds.

A few more things in this same neighbourhood that got flagged as “explain this clearly or someone will burn a day on it”:

  • The internal load balancer’s health probe needs a static route configured on the NVA side, and the FTDv’s HTTP server needs to be enabled with an ACL letting that probe through on the internal interface.
  • Your static routes to the Azure vHub gateway need to stay at metric 1. The NVA isn’t directly connected to the vHub router, so it has to reach it via static route — and if that route’s metric is higher than BGP’s default of 20, you’ll get route flapping.
  • Under BGP advanced settings, check the box for “Disable Connection Verification.” Azure needs it checked.
  • You do not need a user-defined route (a UDR, in Azure-speak) on the vHub side. If you’re hunting for where to add one, stop — there isn’t one. Again, Azure Routing Intent is one-and-done, there is nothing to do on the Azure side of things. Likely the issue is on the NVA side so go back to the vendor NVA documentation and triple check everything.

Sizing Your Hub: The Decision You Don’t Get a Second Chance At

This next part isn’t a “gotcha,” it’s just math that’s easy to skip past during initial design and painful to discover later. Making this error means standing up a new Data Centre or having multiple Data Centres. The networking world is working on 10-20 year cycles, not the faster server world cycles of 5-10 years. We want to make design decisions that last.

Every Azure Virtual WAN hub reserves a fixed pool of IP addresses for NVA subnets, and that pool size is locked in by the hub’s address space when it’s created. It doesn’t matter whether you’re using the capacity or not — it’s static, and changing it later means rebuilding.

Here’s how the address space choice plays out:

vWAN Hub Address Space (for NVA vNet allocation)IPs per NVA subnetMax Scale units per NVA as dictated by Vendor (example Cisco with Cisco’s max throughput figures)Max vHub theoretical limit with all 16 NVAs deployed
/23 or smaller1140288 Gbps
/222780480 Gbps
/215980480 Gbps
/20 or larger12380480 Gbps

Pick a /23, and you’re capped at 288 Gbps hub-wide and 40 scale units per NVA. Go to /22 or bigger and both numbers jump — 480 Gbps and 80 scale units. My recommendation is at least a /22. Honestly, since most organizations aren’t using this private address space for anything else, I’d go as far as suggesting a /20 just to future-proof against whatever Azure changes down the road. It costs you nothing today. The maximum number of NVAs per hub is always 16, regardless of size — so this decision is really about how big each of those 16 can eventually get (Azure scaling with additional VMs), not how many you can deploy.

Flow Limits: The Outage Nobody Notices Coming

If you only budget for bandwidth, you’re going to get burned by this one.

Every VM, and therefore every NVA, has a maximum bidirectional flow limit — and for an NVA it is half of what the underlying VM’s rated connection capacity is — and this is a hard spike ceiling, not a long-term average. Blow past it, and connections get dropped. Not politely refused. Just dropped. The client machine keeps retrying a TCP handshake that will never finish, and to the end user, it looks like the app is frozen or spinning forever, with zero indication of why.

This always matters but it matters more if your NVA is doing double duty. An NVA handling both north/south and east/west traffic — which is a pretty normal pattern for an Azure landing zone — is eating into its flow budget from two directions at once, and needs to be sized accordingly from day one, not after the help desk tickets start rolling in. Be mindful of where the backups are going, that’s going to be the big flow generator if it goes via the firewall.

Should You Cluster the FTDvs? My Answer: Probably Not

Azure High Availability is not supported with clustering. That one line should stop you before you get excited about clustering as the “enterprise” answer. In Azure, the only reason to cluster is to auto scale and that introduces complexity most enterprise organizations don’t need.

Without clustering, Azure’s built-in internal load balancer already does most of what you’d want:

  • Traffic is already load balanced to all the VM FTDv instances in the NVA by default.
  • Want to pull a VM FTDv in the NVA out of service? Remove its health probe static route. Done — traffic stops immediately.
  • Scale up and add a new VM FTDv instance? It comes up without an active health probe route, so it stays silent until you deliberately turn it on.

That’s a manual process, sure. But it’s predictable and low-drama, and it doesn’t drag in the cost and operational overhead of a full autoscaling pipeline — which for FTDv means standing up Azure Function Apps and Logic Apps and a whole different deployment process. For a shop that isn’t building toward serious autoscaling, that complexity isn’t buying you much.

Clustering on in Azure with Cisco FTDv also comes with a list of unsupported features so always be careful to read the caveats before implementing . What might not be supported? This is the list for Cisco: remote access VPN (SSL VPN and IPsec VPN, site-to-site VPN, Virtual Tunnel Interfaces (VTIs), High Availability, Integrated Routing and Bridging, to name a few — plus real operational care and feeding: disabling health checks around any topology change, never pulling more than one node out of a scale set at a time, disabling clustering on a node before removing it. None of that is a dealbreaker if you need clustering. It’s just a cost you should go in knowing about.

My take: clustering earns its complexity when you’re actually building toward autoscaling. If you’re not there yet, the built-in load balancer and manual scaling gets you the same outcome with a lot less to manage.

Where This Leaves You

If there’s one idea I want a traditional networking person to walk away with, it’s this: Azure Virtual WAN isn’t hiding half the configuration from you out of carelessness. It already did that half of the work before you logged in. The ASN you never set, the BGP neighbour you’ll never see in the portal, the route table you configure once and never touch again — none of it is missing. It’s just handled.

The engineers who get comfortable with this fastest are the ones who stop hunting for the configuration step that isn’t there, and start trusting the health probes and Routing Intent to do the job that “both sides configured” used to do by hand.

About the Author

Trevor Textor specializes in solving problems that have organizations stuck. That means he does pretty broad things from A-Z and somewhere in there yes, he helps out with networking. Sharing what he learns the hard way is a hallmark of Trevor’s work. Ask Trevor if he can help: anyskill.ca/afc-capability-matrix.

Citizen Development in Practice: My Successful Implementation Story – July 22, 2021 – All Welcome

I am honored to be speaking to up to 2000 members of the Project Management community about Low-Code Citizen Development in Practice on July 22, 2021 from 10-11am MST. Everyone is welcome.

Since this is a non-premium ProjectManagement.com webinar you should be able to sign up with a free account.

For PMP/PgMP and CAPM PMI certified members, the webinar qualifies for 1 PDU (0.5 Technical and 0.5 Strategic).

https://www.projectmanagement.com/webinars/701305/Citizen-Development-in-Practice–My-Successful-Implementation-Story

Topic

Citizen development is gaining traction and many organizations are using low-code or no-code software to build apps and solve business problems. So how should organizations go about implementing citizen development? In this session Trevor will share his experience in implementing a successful citizen development project using a low-code platform.

Trevor will outline the project he implemented from the start through to successful outcomes including;

  • How he approached the project from zero low-code experience
  • Evaluation of the low-code platforms of the day
  • Designing for long-term sustainability
  • Implementation process
  • Key outcomes and success measures
  • Lessons learned during this citizen development project

Come hear how this low-code project worked from start to finish and understand how to use citizen development for your own business project.

Are Home Depot Reviews Trustworthy?

Quality is very important to me and I’ve made the commitment to reviewing products when I can. As a reviewer there are certain things needed to ensure the review is useful and true. Thus, I was able to explore the question “Are Home Depot Reviews Trustworthy?” with a real world experience. That is, it was with great shock and frustration that I encountered Home Depot’s archaic online review policy (homedepot.com, homedepot.ca).

The Background – On the Hunt for an LED porch light

I’ve been on the hunt for about 5 years for an “LED porch light”* but just saying that doesn’t do it justice. If you’ve ever shopped for LED light bulbs, you’ve probably been overwhelmed with the number of specifications you need to keep in mind. Lest you buy the wrong bulb and spend endless trips to the store to find the right one. So, our specification for an LED porch light are:

  • “suitable for damp locations”
  • have a temperature rating of at least -20C (ideally more of course since we live in Canada)
  • at least 100W incandescent equivalent (1500 lumens or more)
  • “A” shaped bulb (A19/A23) – this is the classic bulb shape
  • Medium or standard base (“E26”) – the standard North American light bulb screw-in socket size of 26mm diameter
  • dimmable since most porch lights are on a low-level light until they detect motion and output more lumens
  • colour temperature of 2700K (like an incandescent bulb)

For the last 5 years there have been absolutely no bulbs with these specifications at Home Depot and I’ve been testing various inexpensive LED bulbs from Amazon; some are even only indoor rated! Suffice it to say, they start flickering in the 6-18 month range.  

* As an aside, commercial building’s parking lot lights face a similar complex situation and there are specific outdoor LED light bulb considerations.

LED Porch Light Found at Home Depot

Until recently when I was looking again at Home Depot, I found the “Ecosmart 100W Equivalent Soft White (2700K) A19 Dimmable LED Light Bulb (3-Pack) – ENERGY STAR” (Model # B6A19100WESD01)”. The Home Depot site link for this product can be accessed by clicking here.

It looked good on paper and the online reviews looked ok. The cost per bulb was $7.42 CAD. Quality indoor bulbs are a bit cheaper than this so this seemed reasonable for an outdoor capable bulb. Upon connecting it the first day it seemed to work ok. I posted this review thinking I could modify it later when I had more operating data:

“Rating: 4 out of 5 stars

Subject: Not Listed as “Outdoor” But…

Body: I bought these to use as porch lights; so outdoor. The box says “Indoor” which is opposite from the online listing. It does say “Minimum starting temperature -20 C (-4F)” and “Suitable for damp locations; do not use where directly exposed to water”. I suppose it may be able to be used outside so I’m giving it a try. I’ve installed the bulb in summer and I’ll try to post again how it does through a Canadian winter (-30 to -40 C). It’s really hard to find 100W equivalent 2700K outdoor LED bulbs so beggars can’t be choosers!”

LED Porch Light Goes Wrong

However, within 2-3 days, it started flickering immediately on start-up. With LED bulbs this indicates a shoddy/inexpensive LED controller which is a common issue of cheaper LED bulbs. I’ve encountered this issue with LED bulbs many, many times and because of this it’s rare to achieve the “long operating life” promised by LED bulbs.

The solution, of course, is to source a more expensive bulb. This is usually from specialty lighting stores that are not local. I found a replacement on 1000bulbs.com, which is a site that has a good filtering/search mechanisms for bulbs, and then sourced a somewhat more favorable price on amazon.ca once I knew what I was looking for. The replacement bulb cost $14.07 CAD. The cost, being approximately double, the bulb also came with a -30C rating and a 25,000-hour bulb life (15,000-hour is the typical bulb life). When I plugged it in, you can tell right away it has a quality LED controller.

Are Home Depot Reviews Trustworthy?

Back to my home depot review and answering the question “Are Home Depot Reviews Trustworthy?”. I was excited, so I provided a more favorable review of the the Ecosmart bulb than I should have. But when I asked Home Depot Chat Support to modify or delete it, they quoted me this:

“Home Depot does not guarantee that you will have any recourse through Home Depot to edit or delete any content you have submitted. Ratings and written comments are generally posted within two to four business days. However, Home Depot reserves the right to remove or to refuse to post any submission for any reason.”

This means if a reviewer submits a review, they cannot edit or delete it after. As in my situation, say the product works great day 1 but by day 3 it’s not working, the reviewer has no recourse. You can’t go online and edit your review. You can’t take your review down by deleting it. Instead, you get to look like a chump if you think the product is great and days later it’s a piece of crap. Basically, Home Depot owns your review. Sure, Home Depot is allowing you to “make an honest review written by a customer” but it’s static, which makes it useless. Home Depot moderates all reviews anyhow, so I don’t understand this requirement.

Conclusion on Are Home Depot Reviews Trustworthy?

When I raised the issue of “Are Home Depot Reviews Trustworthy?” on reddit, user ShinyYoshi surmised “I suspect they don’t allow editing or deletion of reviews because they don’t want positive reviews being changed to negative ones or vanishing. From what I have heard, negative reviews don’t even get approved for posting. I would recommend posting/trusting reviews from other sources.”

My recommendation: Avoid Home Depot reviews until they address this issue and rely on reviews on other sites. Amazon comes to mind. You can run Fakespot (fakespot.com), ReviewMeta.com or any other review analyzer to determine the overall trustworthiness of the specific URL’s reviews since fake reviews can creep into any review site despite the sites trying to moderate all reviews.

About the Author

Trevor Textor loves, loves, loves quality products. So much so that he’s been accused of having ugly things that work really, really well. On his journey for quality he has shared his knowledge as a reviewer as a Google Local Guide, which can be viewed by clicking here, and as an Amazon Reviewer, which can be viewed by here. If you’d like to get in touch with Trevor click here.

Is resilience bad? Article reviews.

Is resilience bad? It can be. In another one of life’s ironies, somebody could label you “not resilient” when in fact you might be “too resilient”. Tomas Chamorro-Premuzic and Derek Lusk’s insightful article on “The Dark Side of Resilience” (click here to see article) highlights another humbling highlight of our collective human ignorance. Indeed, everyone should be aware of this reminder of a dangerous psychological bias.

Key quotes that resonated with me from the article:

” …[E]xtreme resilience could drive people to become overly persistent with unattainable goals. Although we tend to celebrate individuals who aim high or dream big, it is usually more effective to adjust one’s goals to more achievable levels, which means giving up on others….[P]eople waste an enormous amount of time persisting with unrealistic goals, a phenomenon called the “false hope syndrome.”

…[T]oo much resilience could make people overly tolerant of adversity. At work, this can translate into putting up with boring or demoralizing jobs — and particularly bad bosses — for longer than needed.

…[The goal is to compete between groups not within the team, so,] …choosing resilient leaders is not enough: they must also have integrity and care more about the welfare of their teams than their own personal success.

In sum, there is no doubt that resilience is a useful and highly adaptive trait, especially in the face of traumatic events. However, when taken too far, it may focus individuals on impossible goals and make them unnecessarily tolerant of unpleasant or counterproductive circumstances. This reminds us of Voltaire’s Candide, the sarcastic masterpiece that exposes the absurd consequences of extreme optimism: ‘I have wanted to kill myself a hundred times, but somehow I am still in love with life. This ridiculous weakness is perhaps one of our more stupid melancholy propensities, for is there anything more stupid than to be eager to go on carrying a burden which one would gladly throw away, to loathe one’s very being and yet to hold it fast, to fondle the snake that devours us until it has eaten our hearts away?’”

Another article by author Jami Attenberg called “Is Resilience Overrated?” (See the full article by clicking here) adds even more fuel to the suspicion fire when wondering “is resilience bad?”:

“‘You’re so resilient’ is just code for ‘You’re on your own, sorry.’

“Is the idea of resilience a scam? A con to get you to do more so others have to do less? My friend Sara Nović joked in a message that “resilience is made up by our capitalist overlords,” and she added a “lol” but I didn’t even laugh — and I don’t think I was meant to.”

The Barriers to Better Internet – Comment and Share!

Where is this tower?
Who owns it?

We all want more Internet in more places. Most folks assume that the stage is set to make this happen. Unfortunately, no it is not. As an Internet builder myself, I can say that, yes, funding is an issue but it’s not the first hurdle. The initial barriers to better Internet involve data. That is, there is no infrastructure map or market to help build the Internet. These are things we need before we can even look at the issue of funding. Let’s explore what I mean.

Explaining the Barriers to Better Internet

I’ll use an analogy because it simplifies things and takes the industry specific terminology off the table. We want to build a house. We have nails but where do we find the wood? There is no equivalent of a home hardware store to go to. Instead what we have are wood piles placed all over the country sitting unused. How do we find the wood piles? Who owns them? What kind of lumber is it specifically? (2×4? 2×6? Length? etc.)

Most first world governments do supply funding but it is typically for building more of these hidden wood piles.

What exactly are these “wood piles”? They are “passive infrastructure” needed to build the Internet. Things like towers, conduits and cables (like fiber). And this infrastructure is shareable; meaning they are more like a 40-story office tower than a single-family home. The nails are active infrastructure like radio and cable transceivers which are readily available. But where do you install these things if you don’t have any passive infrastructure to install them on? How do you create a budget that is reasonable? (That is, not build absolutely everything from scratch; which is how we do it today.) This is the challenge of Internet builders and it affects urban and rural but rural to a much greater extent.

Rural Problem? Urban Problem? First World Problem?

Here in Canada, there is tons of empty passive infrastructure across the nation but it is hard to find, figure out who owns it and then to strike a deal in which to share it.

But based on what I’ve seen, this problem certainly exists in both the USA and Canada and it is highly likely most other jurisdictions around the globe. It is just the degree of the problem that will vary.

Canada has a partial database of passive infrastructure for towers called “Spectrum Direct” but adding information about the towers is an afterthought. That is, its intended use is to track wireless (spectrum) licenses and only collects data on where the radio is as meta data about the license (an afterthought). This doesn’t track any unlicensed wireless or “free” wireless. On a tight budget, which would you expect to be used? This means it doesn’t have data on towers for 10s of thousands of towers. Further, the database doesn’t validate the passive infrastructure information and does not indicate ownership of the passive infrastructure. 

On other geospatial databases, nothing seems to be public and whatever there is a patch-work across provinces. I’ve checked with IHS, Esri and even Bell / Telus. In fact, Telecom companies often don’t even know what they own. In one story, a peer of mine reported a fiber pedestal that Bell owned to Bell. Bell didn’t know about it. It turned out they had acquired a company that owned the fiber and had not incorporated the information into their main geospatial database. This is if they even have a main database? It could be spread across multiple databases. A 2013 article by Esri located here explains how Bell better used GIS. This article does not inspire confidence that telecom companies have excellent geospatial databases.

USA has a bit better database, the FCC’s Antenna Structure Registration (ASR) database, but it only tracks towers above 100’. Nothing about smaller infrastructure that is equally as useful to wireless and will be even more so with 5G. There is nothing about private infrastructure or accessing cable.

In urban locations, my own community specifically, Enmax has been laying empty conduit in alleyways. Telus has been “planning” to lay fiber for at least 7 years, probably more. I know rural communities that have fiber to the premises faster. Are Enmax and Telus communicating about what assets are in the ground? Hopefully? Probably not. So urban situations, a little bit better, but clearly not a lot better.

Ground Truthing is not the Answer

Sure, we could drive around urban and rural Canada “ground truthing” to figure out what is there every single time we want to build more Internet. But not all infrastructure is located along roads. And even if you do find something, often times the infrastructure is physically unmarked with ownership information. I have unmarked boxes in my community in Calgary, in rural areas the problem is infinitely worse.

But should we have to drive around mapping everything every time we have a project to build better Internet? This is a mapping process that takes between 1 to 18 months for every single Internet building project being undertaken in every single jurisdiction, every country, etc. This mapping process has to be completed before applying for funding (including government funding!). It introduces considerable delay and expense.

We’re in the year 2020. Why is this data problem not being addressed? I would hope that it’s crystal clear that this data problem is central to resolving the barriers to better Internet. In my experience though, most people do not know about this. And they are further shocked to hear that the Internet is mostly a low profit margin business.

The Internet is mostly a low Profit Margin Business

I hear you: “Wait? What?”. The money in the Internet is in high density/volume (e.g. smartphones). Every other Internet related business has lower margins. The lower the density, the lower the margin. So cabling households with fiber in urban communities is something Telecom companies only do organically over time unless subsidized. This is why Google Fiber has been so slow to expand and hasn’t built anything for the past four years. It takes a lot of creativity to make the funding work.

The fact is, consumers and businesses do not want to spend a lot of money on Internet. It’s a utility now. The cheaper it is, the better for the economy. So, for rural areas, their exceptionally low density makes the situation incredibly dire. Rural profit margins are usually negative. This is the reason why rural areas are a low priority for Telecom companies. Even with government subsidies to help bring the profit margin above zero, rural projects are still lower priority due to lower profit overall and poor prospects for growth.

Taking Down the Barriers to Better Internet

We need two things:

  1. A government policy requiring all Telecommunication assets to be registered to a no-fee publicly accessible geospatial database. Oil & Gas is already required to do this. They have to register every pipeline, every compressor, every plant, etc. to a no-fee publicly accessible geospatial database. Why shouldn’t Telecommunications similarly have to register?
  2. A marketplace for passive infrastructure; a “rentfaster” site for building the Internet. Need to make an offer someone can’t refuse? This shouldn’t take years. It should take less than an hour. And renting passive infrastructure is already proven to work. That’s why ~70% of the world’s towers are already shared, just not here in Canada; read more about that here.

These items would create a marketplace that would drive Internet growth. It would create a vibrant market that could start solving the problem on its own with less and less government funding and intervention and in less time. Based on all this, where are our respective governments with respect to providing funding and direction to this problem? Canadian government: Zilch. US government: Nothing that I know of.

Next Steps?

Overall, I’m looking for like minded individuals willing to volunteer some time. Possibly next step would be to start a petition but I’d like to discuss and develop this idea. If you can’t do much, please share this message and help me reach out to more like-minded folks. There is no requirement to have technical knowledge in this area and many times cross discipline knowledge is critical.

While We Wait for the Barriers to Better Internet to Fall

I’ve written an article that explains some things households, and sometimes businesses, can do to help improve their Internet service without waiting for the larger forces of the Internet to make things happen. Click here for my article “Forget a bandwidth upgrade! Try these 4 things to make the home internet experience better”.

About the Author

An avid writer, Trevor Textor has been quoted by Reader’s Digest, NBC News, Reviews.com and MarketWatch.com among others. Over the course of 20 years Trevor has designed and built many small rural Internet builds across the globe. “It’s slower than dial-up” is something he knows personally (move mouse, wait 10 seconds, screen re-draw, try again) and has since used his passion to look for ways to help build better Internet. How Trevor pays his bills is as a freelancer providing a “swiss army skillset” and a proven ability to successfully assist many small, medium and large businesses in most areas of their business. Please consider clicking here to ask Trevor and his partner if they can help via their freelancing corporation “Textor Corp.”.

In-Person Workplace Serendipity – All Is Not Lost with Remote Working

In-Person Workplace Serendipity Doesn’t Just Happen

This CBC news article “Working from home makes sense for some, but we can’t afford to sacrifice serendipity” article argues that remote working results in a loss of “In-Person Workplace Serendipity” from “[running] into each other without an agenda, get to talking, and creativity is sparked.” I don’t know. I remain skeptical of this.

My experience with my own workplaces is that there is very little creativity. When a person only interacts with their teammates who are people in the same field, I argue very little serendipity happens. In fact, there are theories about this in that it lacks “creative abrasion” and experiences “group think”.

How To Properly Access Serendipity

Where I’ve experienced serendipity is from “going outside the normal”. That is, attending cross-disciplinary events and getting views from completely different life experiences. It is unlikely most people will get this kind of cross-disciplinary access at work unless they have access to great leadership. The TED talk “The secret to great opportunities? The person you haven’t met yet” explains how this cross-disciplinary approach to networking changes life in what I feel is true serendipity.

Now, of course, the benefits of in-person workplace serendipity depends on the actual work. If a person is in a field that requires constant creativity/building of something it may make sense for in-person interaction… but again, these types of activities benefit usually by working in pairs which may still be able to be done remotely just fine (e.g. “pair programming”). There is a lot of evidence that groups beyond 2 people become less productive.  The article mentions summer students and yes, I agree, in person interactions would work best for summer students. However, saying that a lot is lost by interacting remotely just seems wrong. I myself have supported developing individuals and adapting to what they need remotely has been similar to what I would do in-person.

Perceived Barriers to Remote Working

If you watch the video in this same article Linda Duxbury mentions remote workers don’t have child or elder care. Why?? How is that the fault of working remotely? That sounds like it’s not structured correctly. She does mention that bosses may not be familiar with managing people remotely but again, this comes around to the fact no one has been willing to try it, learn and change on a mass scale until now. This sounds a lot like “we’ve always done it this way why would we change?” thinking.

A related article “Video chats short circuit a brain function essential for trust — and that’s bad for business: Don Pittis” suggests that video meetings are “an inadequate substitute for real-life interaction” causing a phenomenon now referred to as “Zoom fatigue”. As a long time remote worker, I whole-heartedly agree that video meetings are bad. But audio meetings? Us long time remote workers haven’t used video for the most part except for screen sharing.

There are obvious problems with video meetings; Have you noticed that you look at a person’s eyes but they are also looking at your eyes and because the cameras are at different spots it just comes off as awkward? This is why I’ve discussed teleprescence which would resolve this and many other issues. But the fact is, we don’t have access to this technology at the individual level yet. In the meantime, audio is superior to video/audio meetings. That’s why I suggest for productivity purposes that after initially meeting by video that folks move to audio-only. The article agrees by saying “you can make a better judgement from listening to audio alone” versus using video.

In-Person Workplace Serendipity

I believe this is just change at work. I don’t think all is lost with remote working and In-Person Workplace Serendipity won’t get replaced completely by remote working. It will get modified. I believe this experience is giving us the opportunity to learn and grow. For instance, maybe we learn exactly those types of situations of which being in-person leads to true serendipity. Then, I believe we’ll have come through to the other side.

If you’d like more articles on the dangers of like-mindedness, a danger present in most teams, see more here “Why Being With Like-Minded People Is Dangerous”  

About the Author

Trevor Textor has worked in various roles requiring remote work since 1997. Since 2014 he’s been supporting small, medium and large businesses as a freelancer (contingent labor) with a “swiss-army knife”-like suite of skills. In addition to setting up policy, procedures and technology for himself and his partner he has also met this need with clients in enabling their remote work. Trevor has been quoted by Reader’s Digest, NBC News, Reviews.com and MarketWatch.com. Ask Trevor if he can help: https://www.textor.ca/contactme/.

Networking Via Virtual Conferences

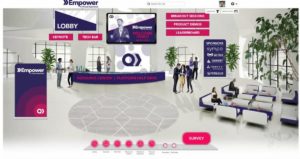
Virtual Conference Lobby

Networking has traditionally been something that needs to be done on the ground. Coronavirus (COVID-19) has thrown a wrench into all that among other things. Like me, you’re probably wondering what it’s like to do networking via virtual conferences?

Background

As a freelancer I get most of my business from networking at conferences. Therefore, I am motivated on a survival level to see if the value of conference networking can be recreated virtually.

My first successful virtual networking experience was via QuickBase’s 2020 Empower Conference. I was specifically looking to experience the networking component as I’ve attended virtual networking in prior conferences and it was a failure. In those instances, the software was not ready for virtual conferences.

Networking Via Virtual Conferences – How It Worked

QuickBase utilized the 6Connex Virtual Event Software. Networking was via Breakout sessions. The participant was given a list of networking subjects to choose from. QuickBase is a low-code platform marketing to the economy as a whole. Subjects included: “manufacturing”, “small business”, “not-for-profit”, etc.

After selecting the subject, the participant was then asked to register their name and email address for a Zoom meeting. Once this was done, the participant was given a Zoom meeting URL. When fully connected to Zoom, the participant briefly met with the conference organizer panel that was assigned to that subject. The panel then randomly assigned the subject to a micro-breakout session of 4-6 people.

The micro-breakout networking ended abruptly at the allocated time. If anybody was mid-sentence they were cutoff. The panel organizers followed the micro-breakout by addressing everybody in the larger audience (~45 people) as a wrap-up and terminated the session.

I arrived late, due to work commitments, so presumably the panel organizers prefaced the subject before assigning people to micro-breakouts.

Lessons Learned

  1. Prepare your workspace for remote working. I wrote a tips article on this subject: https://www.textor.ca/preparing-for-remote-working/
  2. If you know before-hand what the conference is using for video conference software, try to pre-install it. Zoom is very popular though, I suggest having it pre-installed either way: https://zoom.us/download
  3. Test audio and video prior to joining if possible or given the opportunity to do so.
  4. Be ready to video conference.
    • Wear clothes as if you were going into an office.
    • Make sure the background behind you is tidy.
    • Avoid use of virtual backgrounds. In my experience as a public speaker and having been given feedback, they are distracting as they do not work that well. This experience has been consistent over many types of webcams and video conference platforms.
    • Enabling video adds to your perceived level of professionalism. Many folks may not enable their video and that’s ok. But if you want to display professionalism, start with your video on when networking via virtual conferences.
  5. Be familiar with how to mute and unmute. It’s best practice to mute when you are not talking and unmute when talking. I can’t stress this enough and if you only make one thing a habit when working remotely it is this.
  6. Be prepared to take notes. This helps you follow the conversation and ask interesting questions during the networking session. This is something we may not have the opportunity to do in real life, so take advantage of it. I’ve used this technique when publicly speaking on panels and it has noticeably improved my performance over those panelist who do not do this.
  7. Write all the people’s names down in order to follow-up via chat post-call if necessary. The conference usually has a directory so you may be able to track them down to follow-up on conversation items and/or exchange business cards (virtually of course).
  8. Keep to the schedule. Look for an opportunity to ask if there is an interest in swapping contact info. Leave this no later than 5-7 minutes before the scheduled end if possible.

Conclusion

Honestly, the hard stop was frustrating but I can see the value of having this power to “pull the plug” from a conference organizer’s perspective. Clearly, it will take some getting used to networking via virtual conferences. But I see that it can be effective.

I’d like to hear from other’s experiences. What do you think?

About the Author

An avid writer, Trevor Textor has been quoted by Reader’s Digest, NBC News, Reviews.com and MarketWatch.com among others. As a freelancer Trevor has a “swiss army skillset” and has proven able to successfully assist many small, medium and large businesses in most areas of their business. Ask Trevor if he can help: https://www.textor.ca/contactme/.

“The Internet” – UofC Alumni Online Speaking Engagement – May 7, 2020 – All Welcome

I am honored to be speaking to my University of Calgary Alumni association, Computer Science Chapter, on May 7, 2020 from 5:30-6:30pm. Everyone is welcome.

Topic

The Internet. Big, bold, confusing and, most now say, critical.

Trevor Textor has journeyed through the world of “the network” for nearly 20 years. In this presentation he’ll be looking at the Internet from the lens of a rural municipality that had to build their own network just to get the vendor to provide service to their residents. Together we’ll explore the Internet’s many facets and hopefully dispense with a few myths.

Registration

If interested in attending please register here: https://netcommunity.ucalgary.ca/CPSCAlumniLecture_May2020

Update (May 10, 2020): Video recording is located here:  https://www.youtube.com/watch?v=rz0_oj5Balk

Massive Upgrade to Canadians’ Internet Security – CIRA Canadian Shield

Canadians’ Internet Security Gets Leveled Up

“Built by Canadians for Canadians” CIRA’s Canadian Shield effort is a massive enterprise-grade security upgrade for all Canadians’ Internet Security that adds another layer to our collective tool-kit. Implemented with help from the Canadian Security Establishment (CSE), the initial “go live” was 23Apr2020 and presumably this roll-out was fast-tracked due to #Coronavirus #COVID19 elevated threat levels.

How to Turn It On

To enable, users will need to manually update their systems to get the benefit. As explained here, for every system but mobile (explained below), users just need to update their home router DNS settings. This means that users will not have to install and maintain software to get the security benefit.

Note: Some users may have to additionally modify computer DNS settings if they use a manual IP (advanced).

How Canadian Shield Works

Canadian Centre for Cyber Security (CSE) has a nice diagram that shows how it uses DNS to protect users from malicious content.

What is DNS? It’s the thing that translates human readable URLs like “Textor.ca” to an internet protocol (IP) “64.90.34.49”. You can read more about what DNS is here.

Canadian Shield has three levels of service based on the level of protection the user chooses.  The level of protection is determined by which IP addresses the user chooses to configure their DNS with. The three levels are:

  1. Private: DNS resolution service that keeps your DNS data private from third-parties.
  2. Protected: Includes Private features and adds malware and phishing blocking.
  3. Family: Includes Protected and Private features and blocks pornographic content.

Benefits

What I like about Canadians’ Internet Security newest addition is that it’s a non-ISP based Canadian DNS service. Currently the DNS servers are located in Montreal, Toronto and Vancouver and Alberta may need to route via Seattle to get to these services. This makes me skeptical that it will remain fast so I’ll keep this entry posted with updates. The devil is in the details.

OpenMedia.org believes the service is better because “…Canadian Shield … is entirely hosted in Canada, so unlike most free and paid alternatives your Internet data will not travel internationally and become subject to foreign surveillance practices. We also appreciate CIRA’s promise that any information related to your Internet activity is deleted after 24 hours, in contrast to many home ISPs who otherwise handle our web traffic which retain that data longer, or may not guarantee to delete it at all.”

Mobile Users

At home, mobile users will pickup DNS settings from their home router. The challenge is when they are away from home.

For mobile users away from home, my understanding from reddit.com is that users install a CIRA app that enables a VPN. This may be fine for light users but likely will create a bit of havoc for advanced users and their configurations. A reddit users says “Tested the VPN app (iOS) today. First thing I always check is performance. Downstream speed took a hit, upstream was 10% of normal. I’ll skip it for now.” On the Google Play store app a user’s feedback is that it “Blocked access to safe programs” and CIRA asked the user to follow-up by emailing them at CanadianShield@cira.ca.

I’m recommending all users avoid the mobile software for a couple of months to let users that are ok with beta testing work out the bugs.

Update June 17, 2020

Back on April 27, 2020 I implemented the DNS changes to my household router and two workstations that have static IP setups. So far, no issues; as expected.

About the Author

An avid writer, Trevor Textor has been quoted by Reader’s Digest, NBC News, Reviews.com and MarketWatch.com among others. As a freelancer Trevor has a “swiss army skillset” and has proven able to successfully assist many small, medium and large businesses in most areas of their business. Ask Trevor if he can help: https://www.textor.ca/contactme/.